Vigil
Azure Synapse pipeline monitoring and reporting
Know every morning whether your Azure Synapse pipelines ran, with a timestamped, audit-ready record of every run. Free and open source.
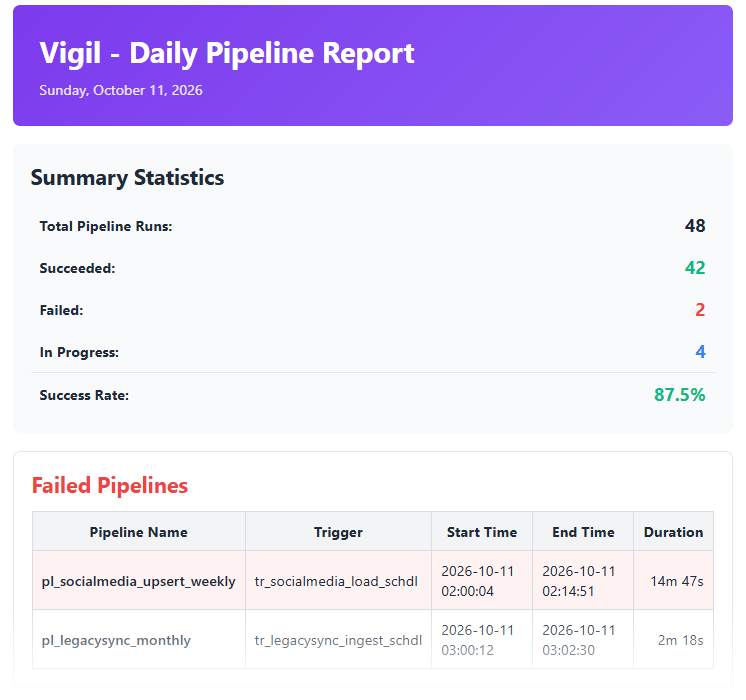
Deploy once. Receive a pipeline summary every morning. Vigil sends a structured HTML summary via Azure Communication Services and archives timestamped CSV snapshots. Teams get fast failure visibility while preserving a durable operational evidence trail.
The daily report email Vigil sends each morning.
The problem
A pipeline that fails quietly is the expensive kind.
Data platforms tend to fail in silence. A Synapse pipeline errors overnight and nothing downstream notices until a dashboard is wrong or a report lands late - by which point you’re explaining the gap instead of catching it. In regulated environments you also have to show you were watching, not just say so.
Vigil makes that watching automatic. Deploy it once and it sends a structured health summary every morning, then archives a timestamped CSV snapshot as an evidence trail - fast failure visibility for the team, and a durable audit record for everyone who asks.
We built Vigil for our own client platforms, and we run it on the ones we deliver.
How it works
From deploy to a daily evidence trail - in four steps.
- 01
Deploy once into your tenant
Vigil runs as an Azure Function inside your own Azure environment. It authenticates with managed identity, so there are no secrets to store or rotate.
- 02
It checks Synapse on a schedule
On a timer trigger, Vigil pulls the last day's pipeline runs from your Synapse workspace - statuses, run IDs, and durations - with no manual polling.
- 03
You get a summary every morning
Vigil emails a structured HTML health report via Azure Communication Services to your chosen recipients: what succeeded, what failed, and the detail on-call needs to act.
- 04
Every run is archived for audit
Each run writes a timestamped CSV snapshot, building a durable evidence trail you can keep for audits.
Built managed-identity-first on Azure Functions and Azure Communication Services - the same platform services your team already trusts, with nothing new to secure.
Who it’s for
Built for teams that must prove pipeline reliability daily.
Data Platform Operations Teams
Get a daily, timestamped summary of pipeline health without building custom monitoring infrastructure from scratch.
Synapse Workspace Owners
Track failed runs quickly with run IDs and durations so on-call engineers can move directly from alert to action.
Compliance-Driven Data Teams
Produce timestamped daily CSV snapshots and structured logs you can keep as an audit record.
Quick start
First report in under 20 minutes.
Provision a Synapse workspace, an Azure Communication Services email resource, and a storage account, then configure local settings, authenticate with Azure CLI, and start the Azure Functions host.
- Python 3.12+
- uv, Azure CLI, and Azure Functions Core Tools
SYNAPSE_ENDPOINT,ACS_ENDPOINT,SENDER_ADDRESS, andRECIPIENT_ADDRESSESconfigured
Current limitations
- Azure Synapse pipelines only (not Azure Data Factory or Microsoft Fabric).
- Email is the only alert channel.
# 1. Clone and install dependenciesgit clone https://github.com/AtLongLastAnalytics/vigil.gitcd vigiluv sync --group devcp local.settings.json.example local.settings.json# Fill SYNAPSE_ENDPOINT, ACS_ENDPOINT, SENDER_ADDRESS, RECIPIENT_ADDRESSES# 2. Authenticate and run locallyaz loginfunc start# 3. Trigger the function (PowerShell)curl.exe -X POST http://localhost:7071/admin/functions/vigil_monitor ^ -H "Content-Type: application/json" -d "{}"# 4. Tests and lintuv run pytest tests/ -vuv run ruff check .
FAQ
Common questions.
Why not just use Azure Monitor alerts?
Can we use Vigil commercially?
What does a customization engagement look like?
Do we own the custom features we pay for?
Do you offer support contracts for the free open-source version?
Private deployments and custom monitoring.
We deploy and extend Vigil in your environment with custom alerting and reporting.