Built for our platforms.
Free for yours.
VISaR
Vulnerability Identification, Scanning & Reporting
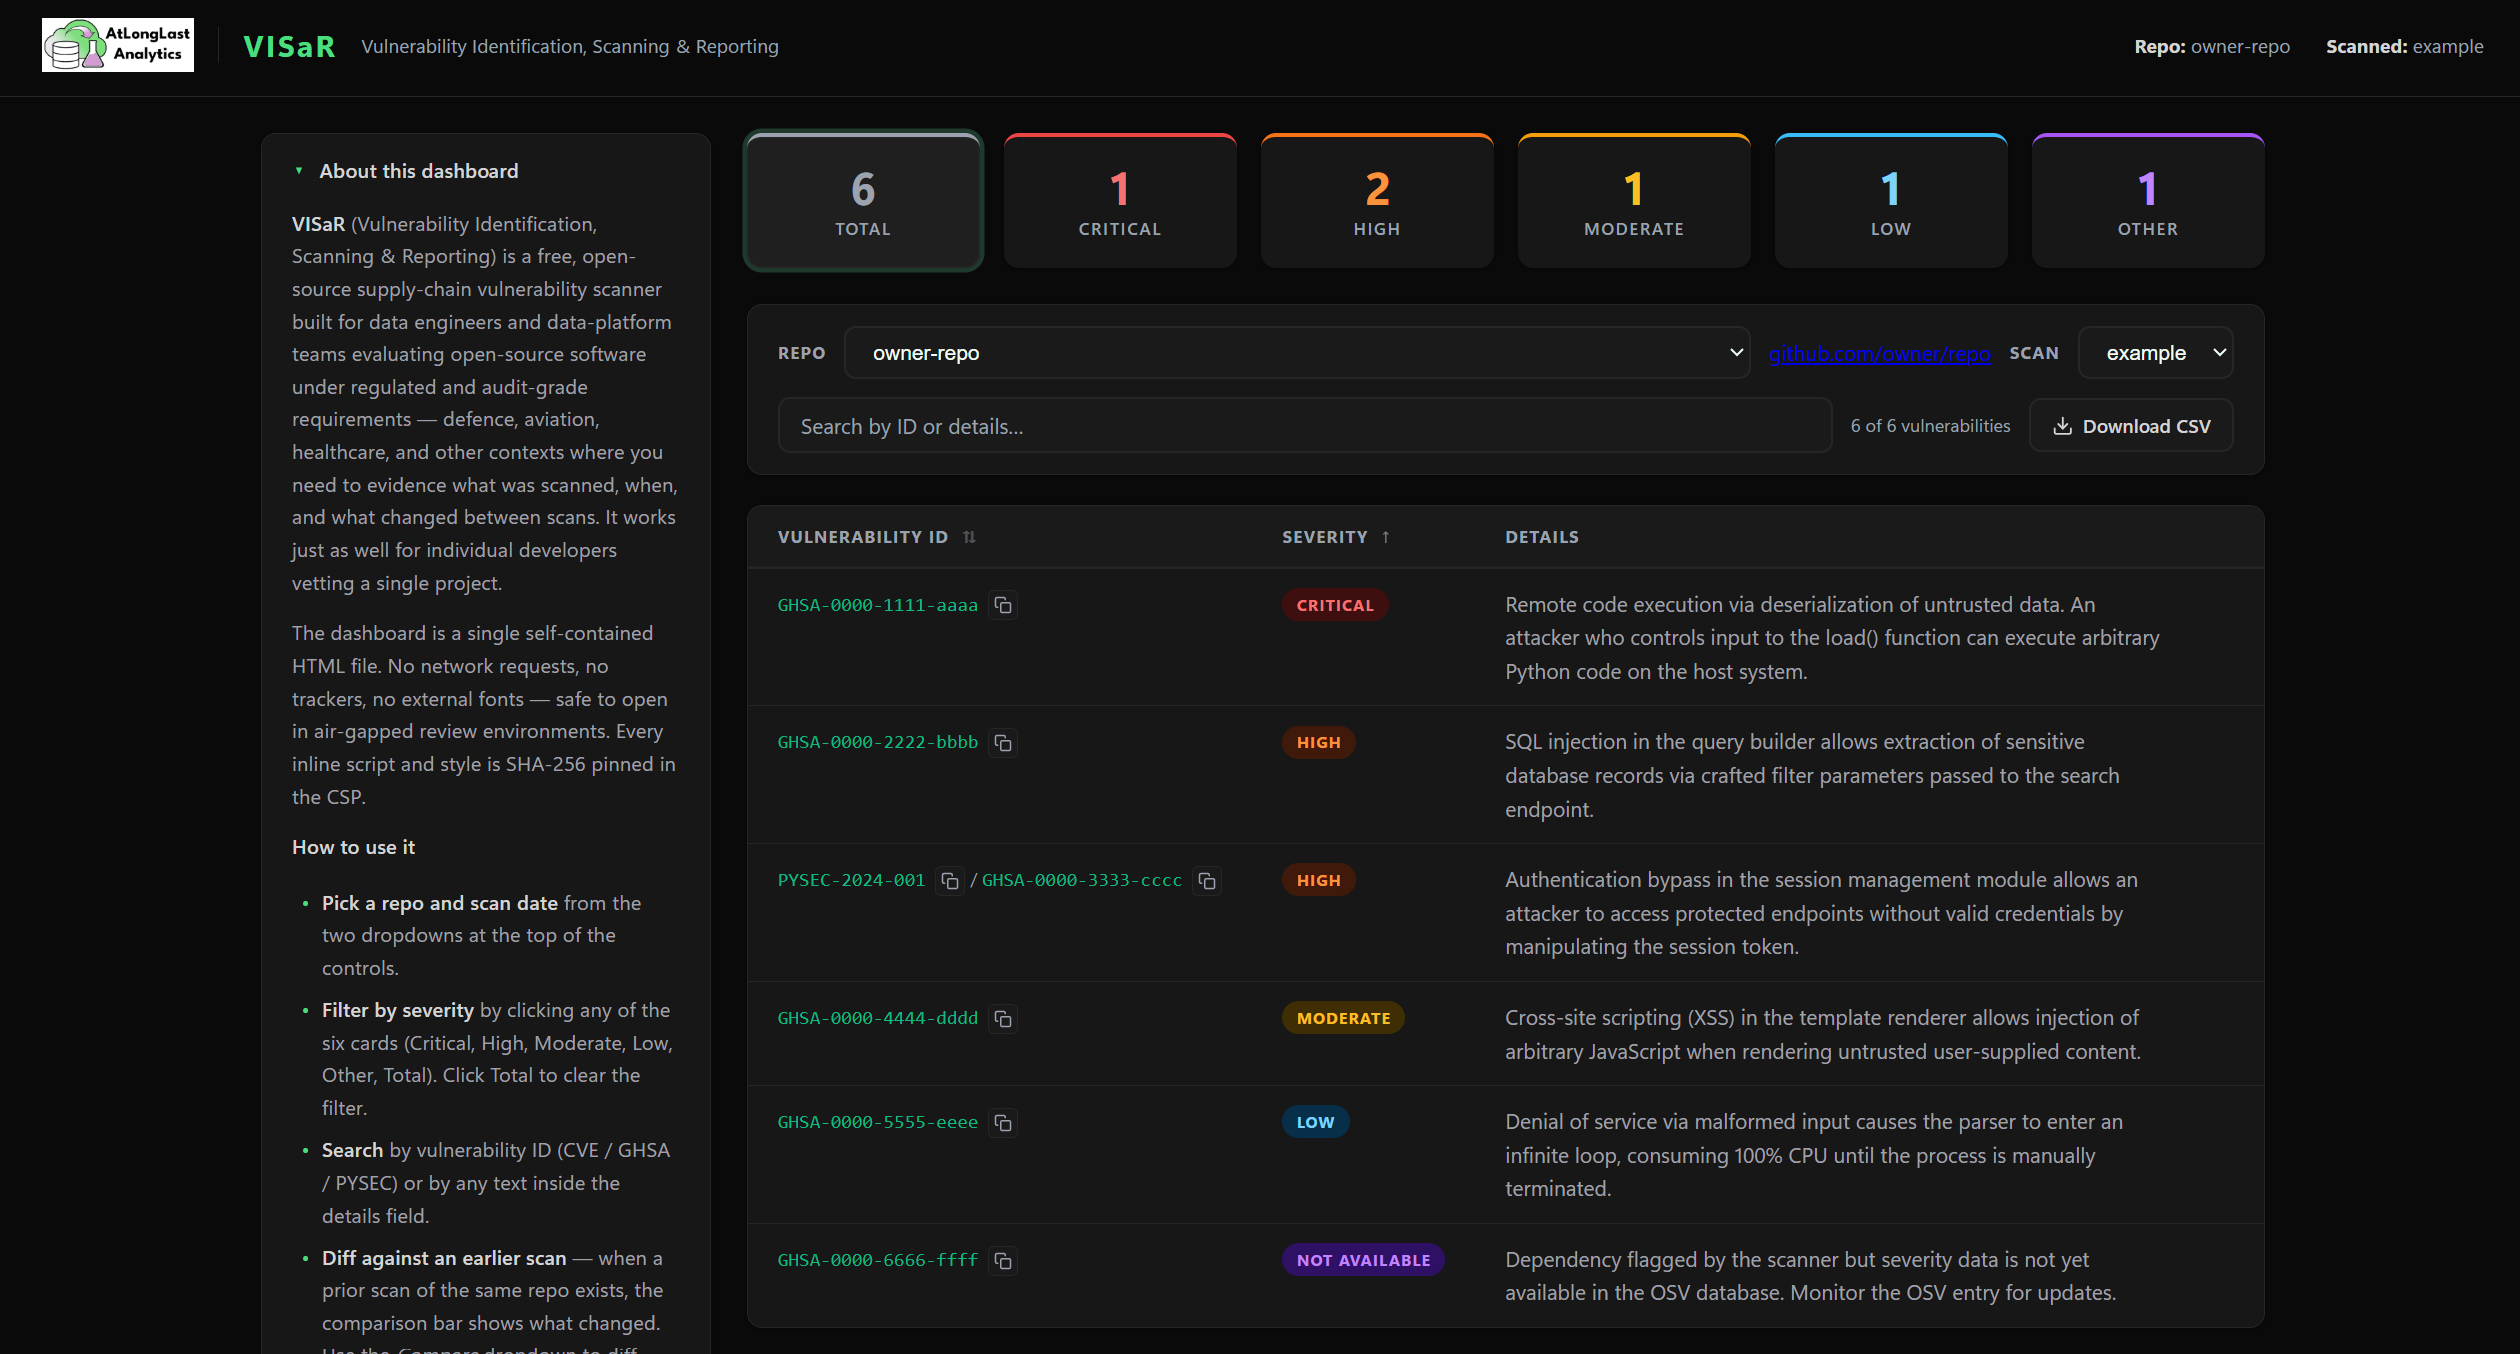
Free, open-source vulnerability scanning that turns dependency vetting into a repeatable command. Scan any GitHub repository against OSSF Scorecard and OSV, then keep a severity-rated evidence record before approving open-source into your data platform.
Vigil
Azure Synapse pipeline monitoring and reporting
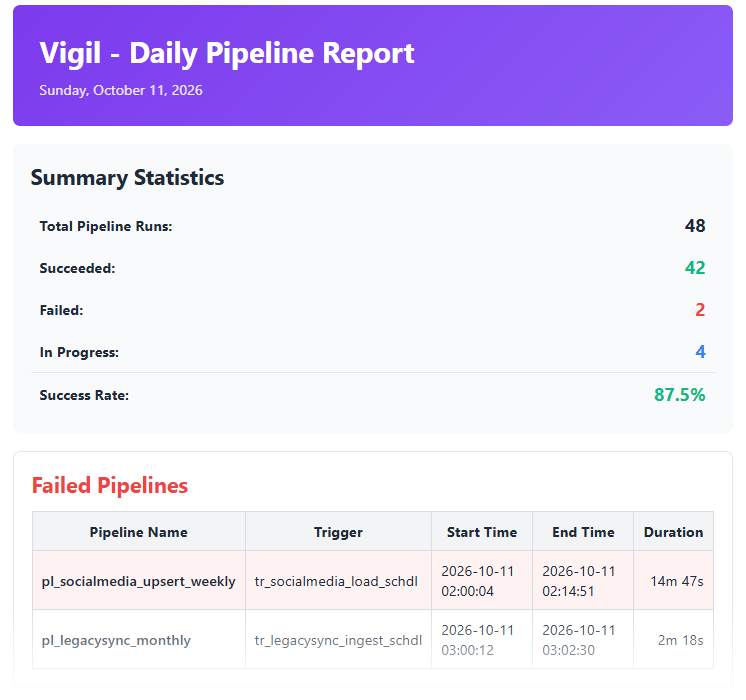
Know every morning whether your Azure Synapse pipelines ran. Vigil emails a daily health summary to your team and keeps a timestamped, audit-ready record of every run.
Free and supported
Use it yourself, or let us run it.
Free to use
Apache 2.0 licensed. Clone it, run it in your own environment, and change it however you need.
Private deployment
We install and configure it inside your security boundary, wired into your platform and controls.
Custom features & support
Extensions and integrations for your stack, plus ongoing support with a named engineer.
Vigil: Daily Pipeline Health Reporting for Azure Synapse
Vigil is a free, open-source Azure Function that checks your Synapse pipelines every morning, emails a health summary, and keeps a timestamped record of every run.
VISaR v1.1.0: Batch Scanning and Interactive Dashboard
VISaR v1.1.0 adds batch scanning across multiple repos and a self-contained HTML dashboard for sharing results. No server, no setup, just a file your team can open and explore.
VISaR: A Code Scanning Tool for Data Platform Engineers
VISaR is a free, open-source tool for scanning GitHub repositories against known vulnerability databases. Built after a client asked how to quantify their open-source risk.
Custom tools for
regulated environments.
Off-the-shelf tools don’t always fit. We build internal tools tailored to your architecture, controls, and security policies.